
Security that holds up as you scale
We do the engineering that keeps your product and your users' data safe: secure architecture, testing that surfaces the weak spots, and the everyday practices that keep it that way as you grow.
What security engineering covers
Finding what's exposed, fixing it, and building so less gets exposed next time. Not fear, just the quiet confidence of knowing where you stand.
Security assessment
Reviewing an application and its infrastructure for what an attacker would find.
Penetration testing
Testing your defenses the way someone trying to break them would.
Secure architecture
Designing systems so a single mistake doesn't turn into a breach.
Authentication and authorization
Getting identity, access and permissions right, where most real breaches actually start.
Compliance readiness
The technical work behind SOC 2, HIPAA, GDPR and the standards your market asks for.
Security in the pipeline
Dependency scanning, secret detection and checks that run on every change.
DevOps & Cloud hardens the infrastructure. Backend Development builds the services this protects.
What we work with
Application security
Identity and access
Cloud security
Testing
Data protection
Pipeline security
Compliance
How we work it
Find what's exposed
We start with a clear look at the application and infrastructure, so the work is aimed at real risk instead of a generic checklist.
Fix by priority
We rank findings by what they'd actually cost if exploited, and fix the ones that matter before the ones that only look scary.
Keep it from coming back
We put scanning and checks into the pipeline, because security that depends on someone remembering is security that eventually lapses.
Who does this work
Security Engineers
Assessment, testing and the hardening work.
Security Lead
Threat modeling, priorities and the compliance path.
Where this capability fits
Success cases
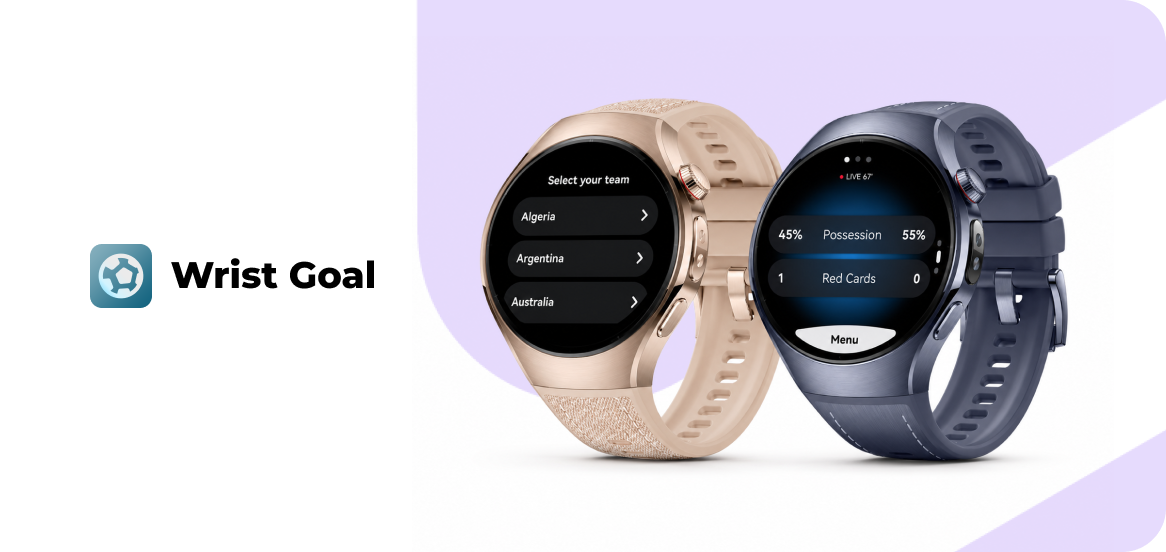
Wrist Goal is a smartwatch app delivering live football scores and match events to Huawei wearables, built by Somnio and launched natively on HarmonyOS NEXT with a template-based architecture ready to scale to future tournaments.

We partnered with the Canadian Automobile Association (CAA) to elevate member services through technology, delivering a seamless experience across Ontario.
What our clients say
“Their approach started with a Product Discovery phase, including user research, UI/UX design improvements, and technical assessments to ensure scalability. Their proactive work made a real difference in the project's success”
“Somnio Software has delivered an MVP that meets the changing needs of AI users. They've communicated effectively, have been highly responsive, and their project management is excellent. Their developers have become thought partners.”


Ready to Start Your Journey?

I would love to talk to you about your project or needs.
Fill in the form or send us an email to hello@somniosoftware.com
Got an idea? We’ve got the skills.
Fill out our contact form and we’ll get in touch!
Schedule a call
Feel free to select a time at your convenience!
FAQs
Still have some doubts?
No worries, here are some frequently asked questions that may help you.
Security engineering is the practice of building software and infrastructure so they resist attack, and testing them to confirm they do. It covers secure architecture, access control, testing such as penetration tests, and the pipeline checks that keep new code from reintroducing old risks.
Penetration testing is an authorized simulated attack on your application or infrastructure, run to find vulnerabilities before a real attacker does. What you get back is a ranked list of what's exploitable and what it would take to fix, based on evidence rather than guesswork.
Earlier than most teams do, and it's a lot kinder to the budget that way. Secure architecture from the start costs far less than retrofitting it after a product, and its exposure, has grown. That said, it's never too late to start, and we'll happily meet your product wherever it is.
We handle the technical side: the access controls, encryption, logging and pipeline work the standards require. The audit and policy side usually involves other specialists, and we'll tell you clearly where our part ends so nothing falls through the cracks.
Yes, and it's common. We review the application, the infrastructure and the access model, then hand you a prioritized list of what to fix, in plain language.